Digital Evidence Management, EnterpriseTube, Security and Compliance, CIO and IT Leadership
 December 9, 2023
Two decades ago, digital evidence played a limited role in investigations. Today, it is central to nearly every criminal, regulatory, and internal inquiry. From body worn camera footage and surveillance video to emails, text messages, and cloud records, the volume and variety of digital data have expanded dramatically.
The National Institute of Justice defines digital evidence as information stored or transmitted in binary form that may be relied upon in court. Its relevance alone is not enough. For digital evidence to be admissible and credible, its integrity must be preserved and demonstrable.
As data volumes grow, preserving evidence integrity becomes more complex. Storage alone is not enough. Organizations need structured systems that centralize evidence, control access, document activity, and maintain chain of custody.
Digital Evidence Management Systems provide this framework. Two controls are central to that framework: metadata preservation and audit logging. Metadata establishes origin and characteristics, while audit trails document how evidence is accessed and handled over time. Together, they support authenticity, accountability, and continuity.
This article examines how these controls strengthen defensible evidence management.

What is Metadata?
Metadata is structured information that describes the origin, characteristics, and history of a digital file.
In a digital evidence context, metadata provides context that the visible content cannot. It may indicate when a file was created, which device captured it, who modified it, or whether it has changed since collection. In many cases, metadata becomes central to reconstructing timelines or validating authenticity.
Unlike ordinary file storage environments, digital evidence systems must preserve metadata exactly as captured. If metadata is altered, overwritten, or inconsistently retained, evidentiary reliability may be compromised.
This is why metadata in Digital Evidence Management is not simply descriptive. It is foundational to credibility.
What Are the Types of Metadata You Should Know About?
In digital investigations, metadata generally falls into four categories, each supporting authenticity and context in different ways.
1. File System Metadata
Creation dates, modification timestamps, file size, and ownership details. Often used to reconstruct timelines and validate sequence of events.
2. Embedded Metadata
Data stored within the file itself, such as EXIF information in images or GPS coordinates in video. Helps confirm capture time, device, and sometimes location.
3. Application Metadata
Information generated by the software used to create or edit a file, including authorship fields and revision history. Relevant in authorship or modification disputes.
4. System Generated Metadata
Metadata created by the evidence management system during ingestion and storage, such as upload timestamps and cryptographic hash values used to verify integrity.
Together, these categories establish origin, chronology, and continuity, which are essential in Digital Evidence Management.
Can Metadata Be Used as Evidence?
Yes. Metadata can serve as evidence when it establishes authenticity, timeline, or integrity.
Courts and regulatory bodies increasingly treat metadata as probative, particularly when it clarifies authorship, sequence of events, or confirms that a file has not been altered. However, admissibility depends on reliability. If metadata can be modified without detection, or if its preservation cannot be demonstrated, its evidentiary value weakens.
To withstand scrutiny, metadata must be preserved in its native form, protected against unauthorized alteration, linked to documented chain of custody, and supported by reliable audit logging.
Metadata alone is rarely sufficient. Its strength ultimately depends on the integrity of the system that stores and tracks it, which is where audit trails become essential.
What Are Audit Trails in Digital Evidence Management Systems?
A digital audit trail is a chronological record of activity within the evidence management environment, from the moment evidence is ingested to its final disposition.
It documents how digital evidence is accessed, handled, shared, exported, or administratively modified. In practical terms, it creates an accountability record for every interaction with evidence.
When evidence is reviewed in court or by regulators, the focus often shifts to process. Who accessed the file. Was it altered. Was it exported outside authorized controls. Were permissions enforced consistently.
A well structured audit trail answers these questions with clarity and documentation.
Audit Trail vs Audit Log
The two terms are often used interchangeably, but they describe different layers. An audit log is the raw record of system events. Each entry confirms that something happened, to which object, and when, but on its own it does not explain the sequence. Turning raw logs into an account of what happened to one file usually takes IT staff to filter entries, reconcile gaps and rebuild the timeline.
An audit trail is that account: the chronological history of an item, case or user, assembled from the underlying records and organized around the evidence and the people who handled it. Investigators, supervisors, attorneys and external reviewers can read it without technical help. Agencies that keep logs but cannot produce a readable trail on request usually discover the gap during a court challenge, a compliance review or an internal investigation, when time is shortest.
How Audit Trails Support Chain of Custody
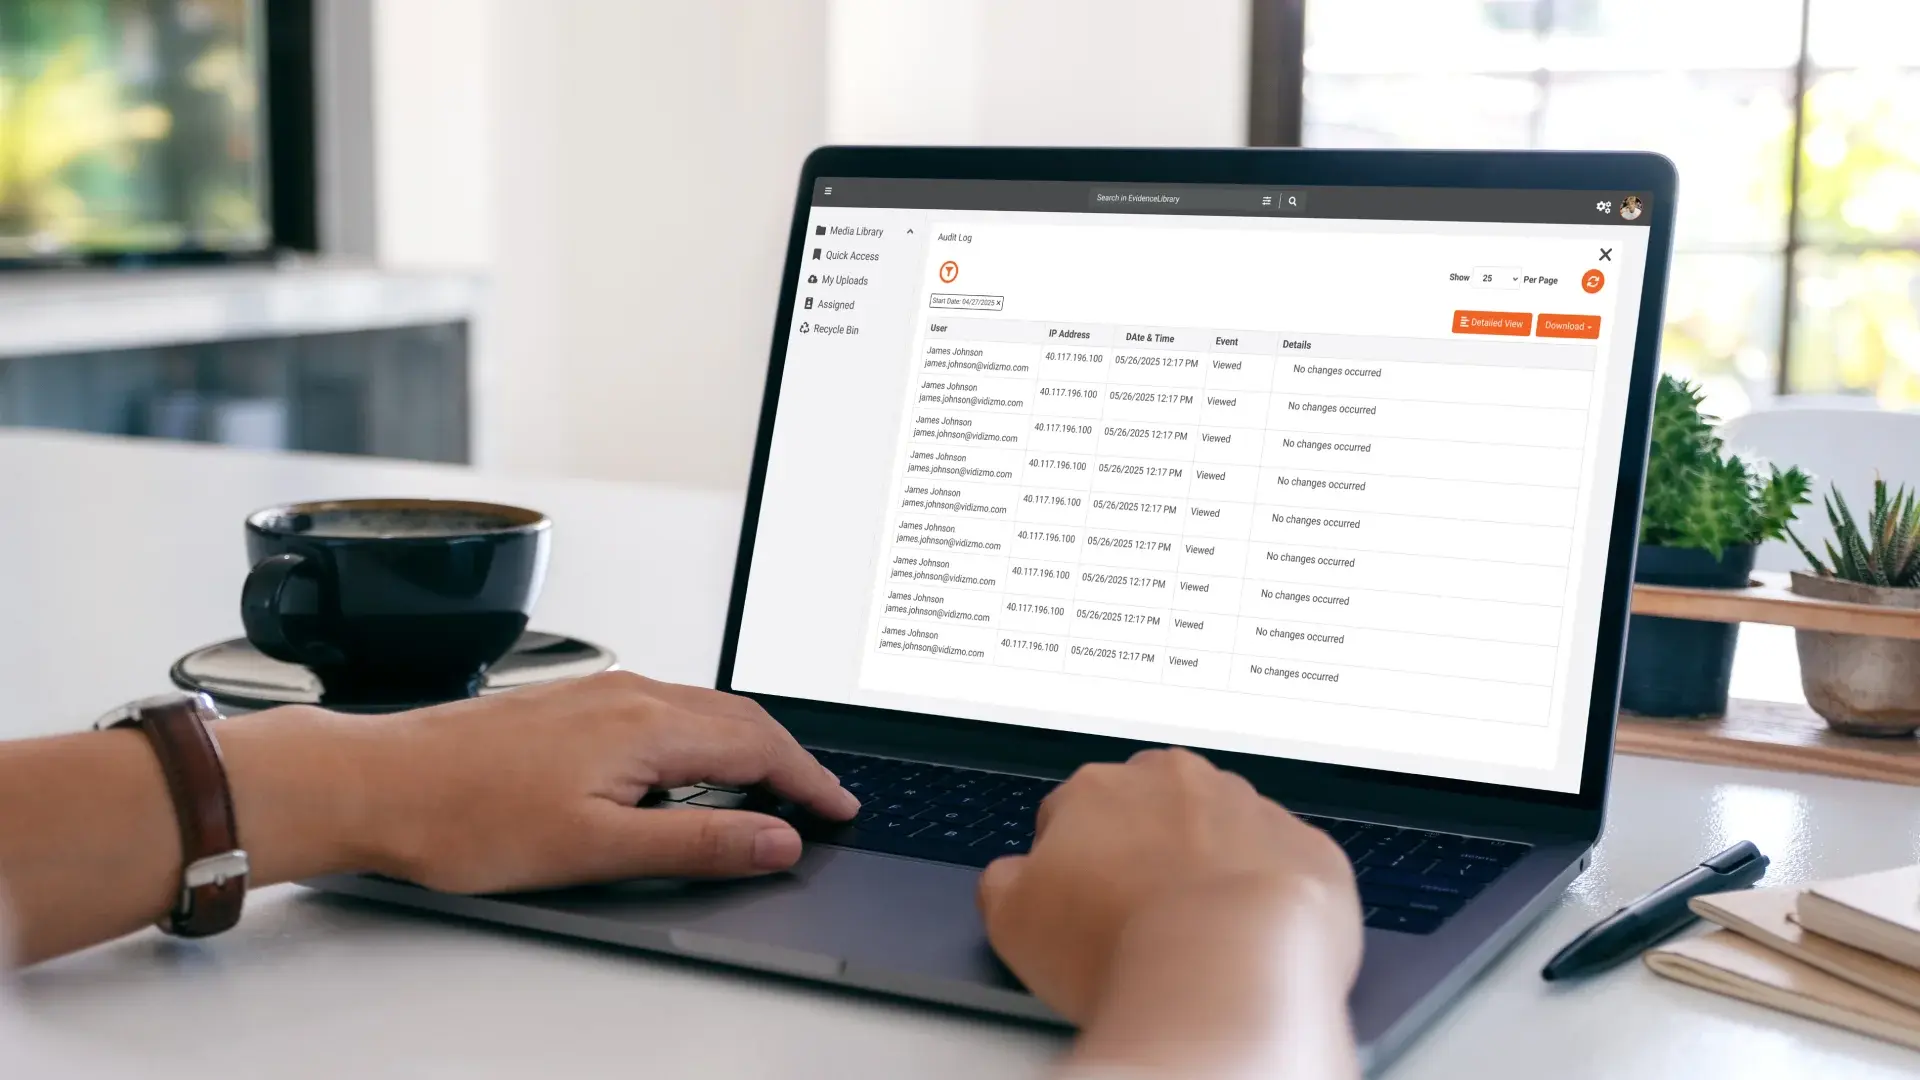
Chain of custody is the documented history of who handled a piece of evidence, when, and why, from collection to court. For digital evidence, the audit trail is that documentation. Each access, transfer, edit, download and share is recorded automatically with the user, the time and the action, so the history never depends on memory or on paperwork reconstructed after the fact.
This is where admissibility challenges tend to land. Defense counsel often targets a gap in custody: a period when no one can show who held the file or whether it changed. A complete audit trail closes that gap, and a hash recorded at ingest and re-verified before trial shows the file has not changed since it entered the system. For the practices that keep custody intact end to end, see our guide to chain of custody for digital evidence.
A typical case: a detective shares body camera footage with a prosecutor, who views it three times over two weeks before trial. The audit trail records the share and each viewing, with the user, the date and time, and the IP address each one came from. If the defense questions the footage, the agency exports that history as a report and presents it alongside the hash verification, instead of reconstructing events from emails and recollection.
What Does an Audit Trail Consist of in Digital Evidence Management Systems?
In a defensible digital evidence environment, an audit trail should capture more than simple access logs. It must document the full lifecycle of evidence handling in a way that supports integrity and accountability.
A comprehensive audit trail typically includes:
1. User Attribution
Every action must be tied to an authenticated user identity. Anonymous or shared account activity weakens accountability.
2. Timestamp Integrity
All events should be recorded using synchronized system clocks to prevent disputes over chronology.
3. Activity Logging
The trail should follow each item through its whole lifecycle and capture both successful and failed attempts. At a minimum, that means five kinds of event:
- Ingestion: when evidence was uploaded, by whom, and from which device or source.
- Access: every view, playback, download and export, including when an AI tool reads or analyzes evidence on a user's behalf.
- Modification: edits, annotations, redactions, clips and metadata changes.
- Sharing: internal and external shares, the recipient, and the access restrictions applied.
- Disposition: retention reviews, legal holds applied and released, and the final transfer, archival or destruction. This part of the record outlasts the case and shows that evidence was neither destroyed early nor kept past its retention schedule.
4. Administrative Oversight Logging
Changes to permissions, roles, retention policies, and system settings must be logged to prevent unnoticed privilege escalation.
5. Integrity Protection of Logs
Audit records themselves should be protected against tampering. In mature systems, logs are immutable or cryptographically secured.
6. Hash Verification Support
Cryptographic hash values generated at ingestion create a digital fingerprint. Revalidation of that fingerprint confirms that evidence has not changed over time. Our guide to how tamper detection works covers the process in more detail.
Evidence-handling standards spell these expectations out. The FBI CJIS Security Policy requires systems that hold criminal justice information to log successful and unsuccessful logon attempts, attempts to access, create, change or delete files, actions by privileged accounts, and attempts to access, modify or destroy the audit log itself. Each record has to establish what happened, when, where, its source and outcome, and who was involved, and records are kept for at least one year. The ACPO Good Practice Guide for Digital Evidence, written for UK policing and widely cited elsewhere, states as its third principle that an audit trail or other record of all processes applied to digital evidence should be created and preserved, and that an independent third party should be able to examine those processes and achieve the same result.
HIPAA, NIST SP 800-53 and ISO/IEC 27001 set comparable logging expectations for health information and for information security generally. In regulated environments, audit depth is not optional. It directly influences evidentiary defensibility.
Organizations handling legally sensitive digital evidence should periodically evaluate whether their audit trail architecture meets both operational and compliance driven requirements before external scrutiny exposes gaps.
Do Metadata and Audit Trails Work Together?
Metadata and audit trails perform different roles, but evidentiary defensibility depends on their alignment.
They work together in the following ways:
1. Authenticity and Accountability
Metadata establishes origin, creation details, and file characteristics. Audit trails document who accessed or handled the file after collection. One confirms what the file is, the other confirms how it was managed.
2. Timeline Validation
Metadata may indicate when a file was created or captured. Audit logs then validate subsequent events such as review, transfer, or export. Together, they create a defensible chronology.
3. Chain of Custody Continuity
Metadata supports initial authenticity, while audit trails document every step in the custody process. If either is incomplete, continuity becomes vulnerable to challenge.
4. Integrity Verification
System generated metadata such as cryptographic hash values can confirm that a file remains unchanged. Audit trails show whether any action occurred that could affect that integrity.
When both elements are preserved and protected, digital evidence demonstrates authenticity, traceability, and procedural control. If one is weak, the credibility of the entire record may be questioned.
What Weak Metadata and Audit Controls Put at Risk
Accountability gaps rarely come from deliberate misconduct. They build up gradually through fragmented handling: a file shared without a record, a permission changed without oversight, metadata lost during a system change. Individually minor, together they leave a file whose history cannot be demonstrated. When that evidence is challenged, three risks surface:
1. Legal Vulnerability
If handling cannot be verified, authenticity is open to question. Even unchanged evidence can lose credibility when its history is unclear.
2. Security Exposure
Without reliable activity records, unauthorized access or misuse is hard to trace, which limits the ability to contain an incident or prove integrity after the fact.
3. Operational and Compliance Strain
Audits slow down when teams have to reconstruct evidence history by hand, and that cost scales with data volume.
These gaps rarely show during routine operations. They surface under scrutiny, which is exactly when they are most expensive.
Embedding Accountability in Evidence Governance
Technical controls only hold if the organization around them is disciplined. Accountability cannot rest on individual diligence; it has to be embedded in how evidence is governed across the whole lifecycle, from collection to oversight. Three commitments make that work:
1. Clear Policies
Documented procedures define how evidence is collected, accessed, transferred, and retained, so handling is consistent rather than ad hoc.
2. Defined Responsibility
Roles and permissions are explicitly assigned, so accountability is traceable rather than assumed. Gaps introduced at collection compound later, so responsibility has to start there and continue through review and export.
3. Continuous Oversight
Supervisors and compliance functions periodically review how evidence is managed, so controls stay effective as systems and personnel change. Small, undocumented deviations are what mature into systemic weaknesses.
When responsibility is continuous rather than segmented, the metadata and audit controls above become institutional accountability rather than isolated features.
Evaluating Metadata and Audit Integrity in Digital Evidence Management
Digital Evidence Management systems vary significantly in how they preserve metadata and enforce audit controls. Superficial feature comparisons often overlook structural differences that affect evidentiary defensibility.
When evaluating a platform, focus on four core areas:
1. Metadata Preservation
The system should retain native metadata at ingestion and generate system level metadata to support classification and lifecycle management.
2. Integrity Verification
Cryptographic hashing should be applied upon upload, with the ability to revalidate file integrity during review or export.
3. Audit Depth and Protection
Granular logging must capture user activity, exports, administrative changes, and failed access attempts. Audit records should be protected against alteration and retained according to policy.
4. Compliance and Deployment Alignment
Logging architecture should support regulatory expectations and maintain consistent timestamp synchronization across cloud, hybrid, or government environments.
Then put these questions to each vendor directly:
- Can investigators, supervisors and attorneys read the audit trail without IT staff interpreting it?
- Does each entry record the user, the action, the date and time, and the IP address it came from?
- Does the trail cover ingestion, sharing, legal holds and disposition as well as access and edits?
- When AI tools read or analyze evidence, is that access recorded in the same trail?
- Is a cryptographic hash recorded at ingest, and can integrity be re-verified on demand?
- Are audit records protected against alteration, and is access to the trail itself restricted by role?
- Can the trail be exported as a report your courts will accept, filtered by user, event or date range?
VIDIZMO Digital Evidence Management System records every action taken on an item in the platform in its chain of custody, with the user, email address, IP address, local date and time, and event, from ingestion to disposition. When an AI agent reads evidence, that access lands in the same trail, attributed to the user who initiated it. With tamper detection enabled, a SHA-384 hash is recorded at ingest and can be re-verified on demand, and the custody trail exports as a formatted PDF report or CSV for court. Technical metadata is captured on ingest, and role-based access controls and log access levels govern who sees the evidence and who sees its history.
If you have any questions or concerns, please leave a message in the comment section below or reach out to us today!

Key Takeaways
- Digital evidence now plays a role in the vast majority of investigations, increasing the need for structured integrity controls.
- Metadata provides contextual proof of origin, timeline, authorship, and file characteristics.
- The main types of metadata include file system, embedded, application, and system generated metadata.
- Metadata can be used as evidence when it is preserved in its native form and supported by reliable audit logging.
- Digital audit trails document who accessed, modified, exported, or administered evidence throughout its lifecycle.
- An audit log records individual system events; an audit trail assembles them into a readable history of each item that investigators, attorneys and auditors can use without IT help.
- A defensible audit trail includes authenticated user attribution, synchronized timestamps, activity logging from ingestion to disposition, hash verification, and tamper protection.
- The CJIS Security Policy requires audit logging on systems that hold criminal justice information, ACPO Principle 3 calls for a record of every process applied to digital evidence, and HIPAA, NIST SP 800-53 and ISO/IEC 27001 set comparable logging expectations.
- Metadata and audit trails work together to maintain chain of custody, validate integrity, and support evidentiary credibility.
- When evaluating a Digital Evidence Management System, integrity architecture matters more than surface level features.
FAQ
Frequently Asked Questions
Can metadata be used as evidence in court?
Yes. Metadata can support authenticity, timeline validation, and file integrity when it is preserved within a secure system that maintains reliable audit logs and chain of custody documentation.
What are the main types of metadata in digital investigations?
The primary types include file system metadata, embedded metadata such as EXIF data, application metadata such as revision history, and system generated metadata including cryptographic hash values.
What is a digital audit trail?
A digital audit trail is a chronological record of user and system activity related to digital evidence handling, including access, modification attempts, exports, and administrative changes.
What should an audit trail include in a digital evidence management system?
A defensible audit trail should include authenticated user attribution, synchronized timestamps, detailed activity logging, administrative oversight tracking, tamper protection, and support for hash based integrity verification.
How do metadata and audit trails support chain of custody?
Metadata establishes the origin and characteristics of evidence, while audit trails document every action taken after collection. Together, they create continuity and accountability throughout the evidence lifecycle.
What is the difference between an audit log and an audit trail?
An audit log is the raw record of system events, with each entry noting that something happened, to what, and when. An audit trail is the chronological history assembled from those records for a particular item, case or user. In digital evidence management, the trail is what investigators, attorneys and auditors read to see who handled evidence and what they did with it, from ingestion to disposition.
What is the purpose of an audit trail?
An audit trail makes every action on a system or record attributable and reconstructable. Its objectives are individual accountability, reconstruction of events, detection of unauthorized access or misuse, and analysis of problems after the fact. For digital evidence it also documents the chain of custody, so an agency can show a court who handled the evidence and, together with hash verification, that the file has not changed since it was collected into the system.
TopicsDigital Evidence ManagementEnterpriseTubeSecurity and ComplianceCIO and IT Leadership
About the author
Moazzam Iqbal is a Product Marketing Executive at VIDIZMO covering digital evidence management, enterprise video solutions, and AI-powered technology. He focuses on helping public safety agencies and government organizations make informed decisions about evidence and video infrastructure.
You may also like
What Is a Real-Time Crime Center? A Guide for Cities and Counties
Somewhere in the last two years, someone probably asked your department whether it should have a real-time crime ...
Staffing a Real-Time Crime Center When Software Does the Watching
Most chiefs who hear a pitch for a real-time crime center ask the same question before any other, which is whether they ...
RTCC, EOC or Situational Awareness Center: What Each Room Is For
Walk into a real-time crime center, then into a city's emergency operations center, and you will see much the same ...