A broken digital chain of custody can compromise the integrity of evidence and lead to courtroom challenges, suppressed files, or complete case dismissals. Because digital files are easy to duplicate, alter, or transfer without detection, a verifiable chain of custody is essential for law enforcement agencies, prosecutors, and digital forensics teams.
When the chain breaks, the evidence loses its presumption of authenticity, the defense gains grounds to challenge admissibility under Federal Rules of Evidence Rule 901, and a judge can exclude it from trial no matter how strong the rest of the case is. Even when broken-chain evidence is admitted, it creates appeal grounds that can lead to retrials or overturned convictions years later.
Digital evidence now sits at the center of most criminal cases. Based on a survey of police chiefs, agency managers, examiners, investigators, and prosecutors, 66% believe digital evidence has surpassed physical evidence. As that reliance grows, so does the exposure: a single undocumented access event or one mismatched hash value is enough to let the defense question whether a file was altered.
This blog covers what a broken digital chain of custody looks like in practice, the legal consequences when it happens, real cases where evidence was thrown out, the factors that commonly cause custody failures, and how a Digital Evidence Management System (DEMS) prevents them.
What Is Chain of Custody for Digital Evidence?
A digital chain of custody is the complete, chronological record of how a digital file is collected, stored, accessed, transferred, analyzed, shared, and eventually presented in court. It confirms that the evidence has remained authentic, unaltered, and fully traceable from the moment it was created or seized.
This documentation goes well beyond a paper trail. It includes cryptographic hash values, preserved metadata, user access logs, system-generated audit trails, and secure storage policies. Together these prove that a file has not been modified at any point in its lifecycle.
How digital chain of custody differs from physical
Physical evidence has the advantage of being tangible. A sealed bag with a signature and date is visible proof that no one opened it. Digital evidence offers no such guarantee. Files can be copied, edited, or corrupted without leaving visible traces.
Timestamps shift. Metadata gets stripped. A duplicate is indistinguishable from the original unless you have a verified hash to compare against. A digital chain of custody achieves through cryptographic and system-level proof what a physical chain achieves through seals and signatures. The principle of continuous, documented control is the same, but the tools are different.
What a Broken Chain of Custody Looks Like in Practice
A broken digital chain of custody occurs when there are gaps, missing logs, unexplained access events, mismatched hashes, or any inconsistency that casts doubt on the integrity of a file. Custody breaks rarely look dramatic. In practice they usually look like one of the following:
- A user accessed the file but the access was not logged
- A SHA-256 hash calculated at intake does not match the hash calculated before courtroom presentation
- Metadata that should have been preserved, such as timestamps, EXIF data, or file system attributes, has been stripped or modified
- The file was transferred between systems without a documented, secure transfer record
- Multiple copies exist with no clear record of which is the original
- The audit log itself has been edited, paused, or restarted
- A user opened the evidence on a personal device, USB drive, or unauthorized workstation
Any one of these is enough for a defense attorney to argue that the file may have been altered. This is the part agencies underestimate: courts do not require proof that tampering actually occurred. They only require reasonable doubt that it could have.
What Happens If the Chain of Custody Is Broken?
A broken chain immediately casts doubt on the integrity of the evidence, and it is one of the most common reasons digital evidence is rejected in court. That doubt cascades through the case in several ways.
The evidence loses credibility
Any gap, missing entry, or unexplained access event invites the court to question whether the file was altered or corrupted. Because digital files can be changed without visible clues, even minor inconsistencies create reasonable doubt and reduce the evidence's value.
It can be ruled inadmissible
Prosecutors must show that evidence is authentic, unaltered, and supported by a documented history from collection to presentation. Under FRE Rule 901, evidence must be properly authenticated to be admissible. Incomplete audit trails, unverified transfers, or missing tamper detection can prevent it from meeting that bar, and a judge can exclude it entirely.
Case outcomes weaken
Without key digital evidence, courts may reduce charges, accept plea deals, or dismiss a case outright. In civil matters, excluded evidence can cost a party the judgment.
Disputes and appeals multiply
A questionable chain gives the defense room to challenge who accessed the evidence, whether it was altered, and how it was stored, which can drive lengthy litigation, retrials, or overturned decisions.
Agency credibility takes the hit
A single mishandled case can raise broader doubts about an agency's entire evidence-handling process, increasing scrutiny on future cases.
Real-World Example: Why Authentication Matters
The consequences of a weak chain of custody are not theoretical. In Griffin v. State (2011), prosecutors tried to use Myspace screenshots to show that a witness had been threatened. The Maryland Court of Appeals ruled the evidence inadmissible because the prosecution could not authenticate it under Maryland Rule 5-901, which mirrors FRE 901. The court noted there was no established connection between the social media account and the person who allegedly created it, leaving open the possibility that someone else had posted the content.
Similar outcomes followed in People v. Lenihan, where Myspace photos used in cross-examination were ruled inadmissible for lack of authentication, and in Meth v. Natus Medical Incorporated, where a LinkedIn profile was excluded under FRE 901 for the same reason. The pattern is consistent. When the handling record cannot show that the evidence is what it claims to be, the court excludes it. The evidence may be genuine, but without a defensible chain the court cannot treat it as such. These rulings predate today's video-heavy caseloads, and courts and rulemakers continue to refine the standards for authenticating digital video and other files.
A domestic example makes the same point for chain-of-custody breaks. In State v. Pulley (2018), the South Carolina Supreme Court reversed a conviction because an incomplete chain of custody, with inconsistent testimony and missing documentation about how evidence was handled and transferred, left the evidence unreliable. The lesson carries directly to digital files, where gaps are even harder to explain away.
Why Digital Chains of Custody Break
Most custody failures trace back to a handful of recurring weak points across the evidence lifecycle.
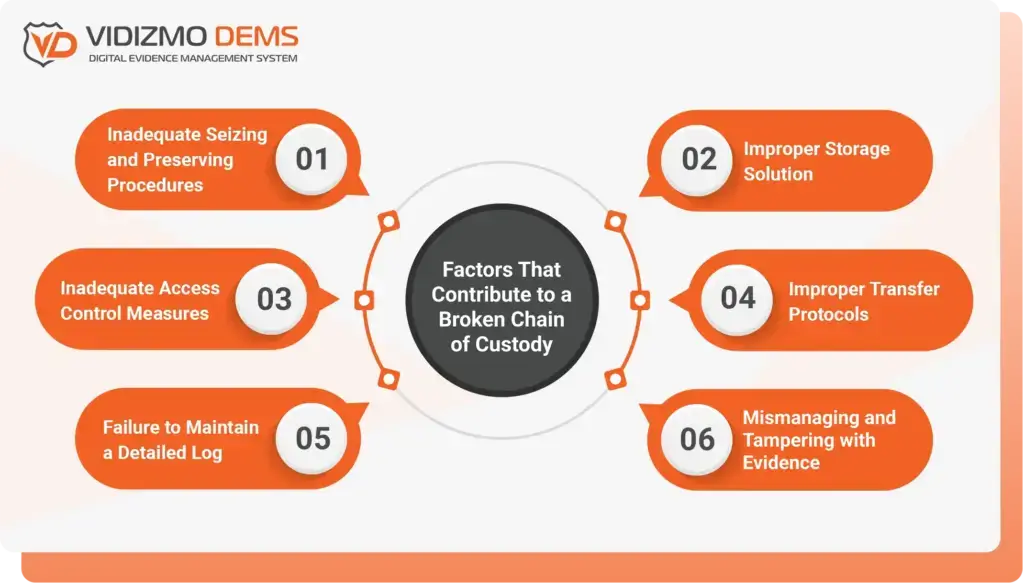
Inadequate Seizing and Preservation Procedures
Failures often begin at collection. If files, devices, or media are not seized with proper forensic procedures, authenticity can be questioned from the start. Evidence must be collected in its original state without altering timestamps, metadata, or file structure, and investigators should work from a forensic image, an exact bit-for-bit replica, rather than the original source.
For a deeper look at this stage, see our guide on how to ensure digital evidence preservation.
Insecure Storage of Digital Evidence
Storing evidence on unencrypted drives, personal devices, shared folders, or uncontrolled media makes it nearly impossible to prove the file stayed untampered. Unprotected storage is one of the most common causes of a broken chain.
Inadequate Access Control Measures
When too many people can reach evidence without clear accountability, or when permissions are not granular, it becomes easy for the defense to argue potential tampering. Access that is not tied to a specific authorized user and a specific permitted action is a liability.
Improper Transfer Protocols
Moving evidence between officers, departments, devices, or agencies is one of the most vulnerable points in the chain. Sending files by email, USB drive, or unprotected cloud sharing creates openings for tampering, loss, or corruption, and leaves no verifiable record that the file arrived unaltered.
Failure to Maintain a Detailed Log
A detailed audit trail is the cornerstone of a defensible chain. Gaps or missing entries mean prosecutors cannot confidently prove the evidence stayed unchanged, and this is one of the most frequent reasons digital evidence is excluded.
Mismanagement or Tampering of Digital Evidence
Any sign of alteration, accidental or intentional, can break the chain. Because digital files can be manipulated without visible traces, integrity depends on compliance with established standards such as the NIST digital evidence guidance, the Federal Rules of Evidence, and the Federal Rules of Civil Procedure.
The Chain of Custody Process, Step by Step
Beyond knowing what breaks a chain, investigators need a repeatable process for building one. A defensible chain of custody is established across four stages.
Data Collection
The chain begins at the scene. Investigators identify and label all relevant digital evidence, such as hard drives, mobile phones, USB devices, or surveillance footage; record metadata, timestamps, and identifying details; and seize devices while keeping them intact and untampered.
Examination
Collected evidence undergoes forensic examination. Every action taken during analysis is documented, modifications or recovered data are captured, and the original evidence is preserved by working only on forensic copies.
Analysis
Using legally justifiable forensic methods, examiners recover and examine relevant data while preserving authenticity, apply forensic tools for recovery and file analysis, and cross-check findings for relevance to the case.
Reporting
The final stage is documentation: every step, including collection, handling, transfer, and analysis, is detailed in the chain of custody report with timestamps and personnel details, and each report is verified for accuracy and legal compliance.
Chain of Custody Step-by-Step Checklist
Use this checklist to keep evidence authentic, secure, and admissible across its lifecycle.
- Identify and secure digital evidence. Locate relevant sources (mobile devices, computers, storage media, cloud data, video systems) and secure them against unauthorized access, alteration, or deletion.
- Document evidence collection. Record the date, time, location, and method of collection, document who collected it, and assign a unique identifier to each item.
- Preserve evidence integrity. Keep the original in its original state, generate cryptographic hash values to establish authenticity, and ensure the evidence remains unchanged throughout handling.
- Secure storage and access control. Store evidence in a controlled, access-restricted environment, apply encryption, and log all access, transfers, and actions.
- Examine and analyze evidence. Use legally accepted forensic practices, document all activities and findings, and keep original evidence separate from analysis outputs.
- Verify and report the chain of custody. Revalidate integrity before transfer or court presentation, maintain a complete chronological record, and ensure documentation is accurate and legally defensible.
How to Prevent a Broken Chain of Custody
Each failure above maps to a control that a Digital Evidence Management System enforces automatically, which is why these practices are now implemented through a Digital Evidence Management System rather than manual recordkeeping.
Automated Chain of Custody Tracking
Manual logs invite missed entries and human error. A DEMS records every upload, access, modification, transfer, and deletion automatically, with a timestamp and the user identity, in a tamper-evident format. The result is a complete chain with no gaps to challenge.
Tamper Detection for Evidence Integrity
Cryptographic hashing such as SHA-256 creates a unique fingerprint for each file. If any bit changes, the hash changes, which makes alteration immediately detectable. A DEMS flags unauthorized modifications in real time and prevents altered files from replacing originals.
Secure Transfer and Handling of Digital Evidence
Handoffs are protected with end-to-end encryption, time-stamped transfer logs, and hash verification before and after transfer to confirm the file arrived unaltered. Sharing across teams and agencies should rely on secure, trackable sharing workflows with time-limited, permission-based links rather than open distribution, with every share and access tracked.
Granular Access Control
Role-based permissions, granular controls over viewing, downloading, exporting, redacting, and sharing, and multi-factor authentication keep evidence in authorized hands. Requiring users to record a reason each time they view, export, or share evidence adds that intent to the permanent audit trail and strengthens accountability.
Lock Down Storage
Evidence at rest should be protected with AES-256 encryption, password-controlled access, and segmented repositories that prevent deletion or overwriting. This ensures files cannot be reached or modified without proper authorization.
VIDIZMO DEMS: Preventing a Broken Chain of Custody
VIDIZMO Digital Evidence Management System brings these controls into one platform. It automates the full chain-of-custody process, recording each collection, upload, transfer, review, and access event with precise timestamps, user identities, and the purpose of the action, which removes the documentation gaps that cause most custody failures.
Stored evidence is protected with AES-256 encryption, password-protected access, multifactor authentication, and granular role-based permissions, so only authorized personnel can view, export, share, or modify files. SHA-based hashing flags any unauthorized modification instantly, while immutable audit logs show who accessed the evidence, when, from where, and why.
Secure sharing is enforced through encrypted transfers, time-limited and permission-controlled links, complete transfer logs, and optional redaction to protect sensitive data. Together these capabilities give agencies, prosecutors, and legal teams a defensible record across the entire evidence lifecycle.
Key Takeaways
- A broken chain of custody can get evidence ruled inadmissible and lead to acquittals, retrials, or overturned convictions, regardless of how genuine the evidence is.
- Digital evidence is uniquely vulnerable because files can be altered, accessed, or corrupted without leaving visible traces.
- The most common causes are improper collection, insecure storage, weak access control, unsafe transfers, missing audit trails, and undetected tampering.
- Courts do not require proof that tampering occurred, only reasonable doubt that it could have, which is why incomplete records fail under FRE 901.
- Griffin v. State and People v. Lenihan show that courts exclude digital evidence when the handling record cannot establish authentication.
- A Digital Evidence Management System prevents these failures with automated custody tracking, encrypted storage, granular access control, and SHA-based tamper detection.
- VIDIZMO Digital Evidence Management System combines these controls in one platform to maintain unbroken custody from collection to courtroom.
Ensuring Evidence Integrity
A broken chain of custody remains one of the most serious risks in any investigation, because it puts the admissibility of otherwise valid evidence in question. The defense against it is consistent: proper collection, secure storage, controlled transfers, and a complete, automated record of every action taken on a file.
A Digital Evidence Management System delivers that through centralized tracking, time-stamped and immutable audit logs, end-to-end encryption, and granular access control, so evidence stays authentic and defensible under courtroom scrutiny.
VIDIZMO DEMS provides this in a single secure, compliant platform. Book a demo to see how it maintains an unbroken chain of custody, or request a free 7-day trial.
FAQ
Frequently Asked Questions
What is the digital evidence chain of custody in forensics?
The digital evidence chain of custody is the chronological record of every action taken on evidence from collection to courtroom presentation. It documents who collected the evidence, who accessed or transferred it, how it was stored, and what forensic actions were performed. Without this documentation, digital evidence cannot be considered legally admissible.
How is the chain of custody for digital evidence different from physical evidence?
Digital files can be altered or corrupted without leaving visible signs of tampering, unlike physical evidence where damage is usually obvious. This is why the chain of custody for digital evidence requires additional steps such as cryptographic hash verification, write-blocking tools, and forensic imaging that are not required for physical evidence.
What are the most common ways a digital evidence chain of custody gets broken?
The most frequent causes include missing documentation at transfer points, working on original evidence instead of a forensic copy, unauthorized or unlogged file access, insecure transfers through email or consumer cloud storage, and mismatched hash values. Any single gap can give a defense attorney grounds to challenge admissibility.
Why do courts require an unbroken chain of custody for digital evidence?
Because digital files can be altered without detection, courts require prosecutors to prove through logs, hash verification, and access records that the evidence presented is identical to what was originally collected. A single undocumented access event is enough for the defense to argue the evidence was manipulated and have it ruled inadmissible.
What information must be recorded in a digital evidence chain of custody form?
A complete chain of custody form for digital evidence must include a unique evidence identifier, date and time of collection, names and roles of everyone who handled it, storage method, transfer records with signatures, hash values verified at each handoff, and a log of all forensic actions performed. Any missing field is a legal vulnerability.
How does cryptographic hashing protect the chain of custody for digital evidence?
Hashing generates a unique digital fingerprint of a file at collection using algorithms like SHA-256. This value is recorded and recalculated at every transfer or analysis stage. A matching hash confirms the evidence is unaltered. A mismatch signals possible tampering or corruption, making the evidence unreliable for court use.
What are the biggest mistakes investigators make with the digital evidence chain of custody?
The most damaging mistakes are analyzing original files instead of forensic copies, skipping hash generation at collection, leaving evidence devices connected to networks, failing to log every person who accessed the evidence, and using unsecured or unencrypted storage. Even leaving a cloned drive unattended in a shared workspace has been argued as a chain of custody violation.
Is there a legal standard agencies must follow for digital evidence chain of custody?
Yes. In the U.S., NIST (National Institute of Standards and Technology) guidelines define how digital evidence must be collected, preserved, analyzed, and reported. SWGDE (Scientific Working Group on Digital Evidence) provides additional forensic standards. Internationally, courts like the ICC use protocols such as the Unified Technical Protocol to evaluate chain of custody compliance.
How does a Digital Evidence Management System strengthen the chain of custody for digital evidence?
A DEMS automates the most error-prone parts of the digital evidence chain of custody, including audit log generation, hash verification, access control, and tamper detection. Unlike general cloud storage, it creates an immutable, court-ready record tracking every action on every file from ingestion to case closure, eliminating the documentation gaps that most commonly lead to evidence being challenged in court.
TopicsDigital Evidence Management
About the author
Sarim Suleman is a Product Marketing Executive at VIDIZMO with deep expertise in enterprise video platforms and digital evidence management. He focuses on helping government agencies and large-scale organizations understand how modern video and AI technology can transform their evidence workflows and operational efficiency.
You may also like
Fire and Smoke Detection as a Second Set of Eyes in Schools
Let the first sentence of this article do the compliance work: nothing described here replaces, modifies, or competes ...
Weapon Detection in Schools: Detection, Verification, Response
No school safety technology carries more emotional weight than weapon detection, and no school safety technology is ...
School Safety Grants: What the Money Can Buy
School safety improvements have a funding problem that is really a sequencing problem: the need is continuous, the ...